PHP2Shell · Node2shell: How Quickly Can Your Organization Respond?
Recently, PHP2Shell and Node2Shell made global headlines, sending security teams scrambling for emergency audits and security patches. This is not the first time. Vulnerabilities found in widely used tech, such as past Log4Shell and React2Shell flaws, have consistently impacted diverse services and entire industries well beyond specific isolated systems.
In particular, unauthenticated Remote Code Execution (RCE) flaws require swift response since attackers can leverage them to seize control of servers. Such threats are not confined to general-purpose software alone. Zero-day vulnerabilities can also surface in niche solutions widely deployed across finance, healthcare, and manufacturing. Identifying and defending vulnerable systems before attackers exploit them is vital.
However, security teams often hit a much more fundamental hurdle than the vulnerability itself.
“Where are the systems running this software in our company, and which assets should we inspect first?”
Even when vulnerability details and patches are released, responding rapidly is difficult if a firm cannot accurately locate its operational assets, deployed tech stack, and versions. Externally exposed services missing from asset inventories or Shadow IT can easily fall through the cracks of vulnerability scans and updates.
Therefore, the key to handling high-risk flaws is not merely discovering them, but continuously mapping the corporate attack surface to quickly pinpoint potentially impacted assets and take necessary action whenever new threats emerge.
High-risk flaws: how did we handle them?

The recently disclosed PHP2Shell vulnerability is a critical security issue tied to the PHP runtime environment. With concerns raised over potential unauthenticated remote code execution under certain conditions, the urgent need for prompt inspection and response has been highlighted.
However, for enterprises, simply understanding technical vulnerability details is not enough. They must identify where their external-facing PHP services are, the environments in which they operate, and which systems require security updates.
As soon as the PHP2Shell flaw was revealed, ENKI Whitehat assessed clients' external assets using its Attack Surface Management service, 'OFFen Managed ASM.' This pinpointed potentially affected systems early, staying a step ahead of attackers.
ENKI Whitehat's ethical hackers analyzed related materials released on October 21, 2026, and briefed clients that evening on vulnerability details and required action.
Such a swift response was possible thanks to the external asset inventory and tech stack data routinely managed via OFFen ASM.
Leveraging pre-existing asset data, ENKI Whitehat reviewed services likely utilizing PHP. It helped clients identify targets needing further review and distributed a proprietary PHP2Shell scanner developed by in-house ethical hackers to verify version and patch statuses in live production environments.
In this way, we empower clients to detect emerging security threats early and review vital remediation measures.
Starting Critical Risk Defense, OFFen ASM

An enterprise external attack surface changes continuously.
Due to new services, cloud expansion, vendor websites, or unmanaged test servers, assets can emerge that security personnel haven't identified.
When new high-risk vulnerabilities are disclosed, staff must first identify affected systems. If finding assets and their owners takes too long, vulnerability assessment and remediation will inevitably be delayed.
To respond quickly to vulnerabilities, you must identify external assets and technology stacks in advance.
Hacker-driven attack surface management, OFFen ASM

Attack Surface Management (ASM) is a security service identifying, monitoring, and managing potential risks and vulnerabilities in IT assets. It helps spot and counter entry points attackers could exploit.
The OFFen platform's ASM gathers externally exposed domains, IPs, and services. Clients can review exposure status and security issues per asset. OFFen ASM locates and manages Shadow IT missed by security teams, reviewing risk and impact to help prioritize action.
ENKI Whitehat has integrated vulnerability research and field experience into OFFen ASM. Whitehat hackers with top awards from contests like DEF CON have embedded know-how from pentesting and red teaming into the scan engine and risk analysis. Experience researching assets and gaps sought by attackers drives this ASM development.
How to organize inspection targets using OFFen ASM
In responding to PHP2Shell, the first step is identifying externally exposed services running PHP and their status. OFFen ASM automatically discovers internet-exposed assets and identifies services and tech stacks to continuously manage your attack surface. Based on this, you can uncover unmanaged assets and identify services that need review regarding this vulnerability.

First, identify externally exposed assets.
Enter seed info like a primary domain, and OFFen ASM scans for external assets and services. Through this discovery process, you can detect Shadow IT linked to the domain that was missing from security inventories. Review discovered assets' exposed services and ports, verify ownership and operators, and bring them under management scope.

Identify tech stacks to narrow down PHP inspection targets.
OFFen ASM identifies technologies running on discovered assets. Security teams can locate PHP-based services and, if versions are known, compare them with versions affected by PHP2Shell to prioritize review targets. For services lacking clear tech or version details, verify actual environments via operators and dedicated scanners.
Check information leaks and vulnerability risks with endpoint scans.
OFFen ASM inspects key endpoints using the security auditing and vulnerability research expertise of ENKI Whitehat hackers. This identifies risk factors on exposed assets that could lead to data leaks or exploits, providing a solid foundation for rapid response to emerging security threats.
Prepare scanner checks based on verified service addresses.
Compile a checklist of domains and access URLs for confirmed PHP-based services. Security and operations teams can then run dedicated PHP2Shell scanners against this list to determine actual PHP versions and patch statuses.
Beyond asset identification: OFFen ASM assesses real attack risks
Attackers do not just look at domains, IPs, ports, and services. They seek actionable paths like admin logins, configuration/backup file paths, CMS/device URLs exposing versions, and unauthenticated APIs. OFFen ASM checks such endpoints, enabling you to move beyond asset discovery to pinpoint concrete security risks.
Scanned endpoints build on paths used by ENKI Whitehat hackers during penetration tests along with dedicated research databases, while also automatically analyzing target architectures to discover unlisted routes. This covers major CMSs, commercial solutions, network/security appliances, version leaks, PII/document exposures, config/backup dumps, and known exploit points, updated with new vulnerabilities and field cases.
Going beyond simple exposure monitoring, OFFen ASM leverages cataloged asset and tech data whenever critical vulnerabilities arise to swiftly identify and remediate affected systems. Without installing agents or writing code integrations, you can inspect exposed assets, prioritize discovered risks, and achieve more effective security management.
Upon deployment, scan all externally exposed assets for risky endpoints without extra installs or dev integration, and prioritize remediation immediately using the provided risk severity levels.
Customer Support Status
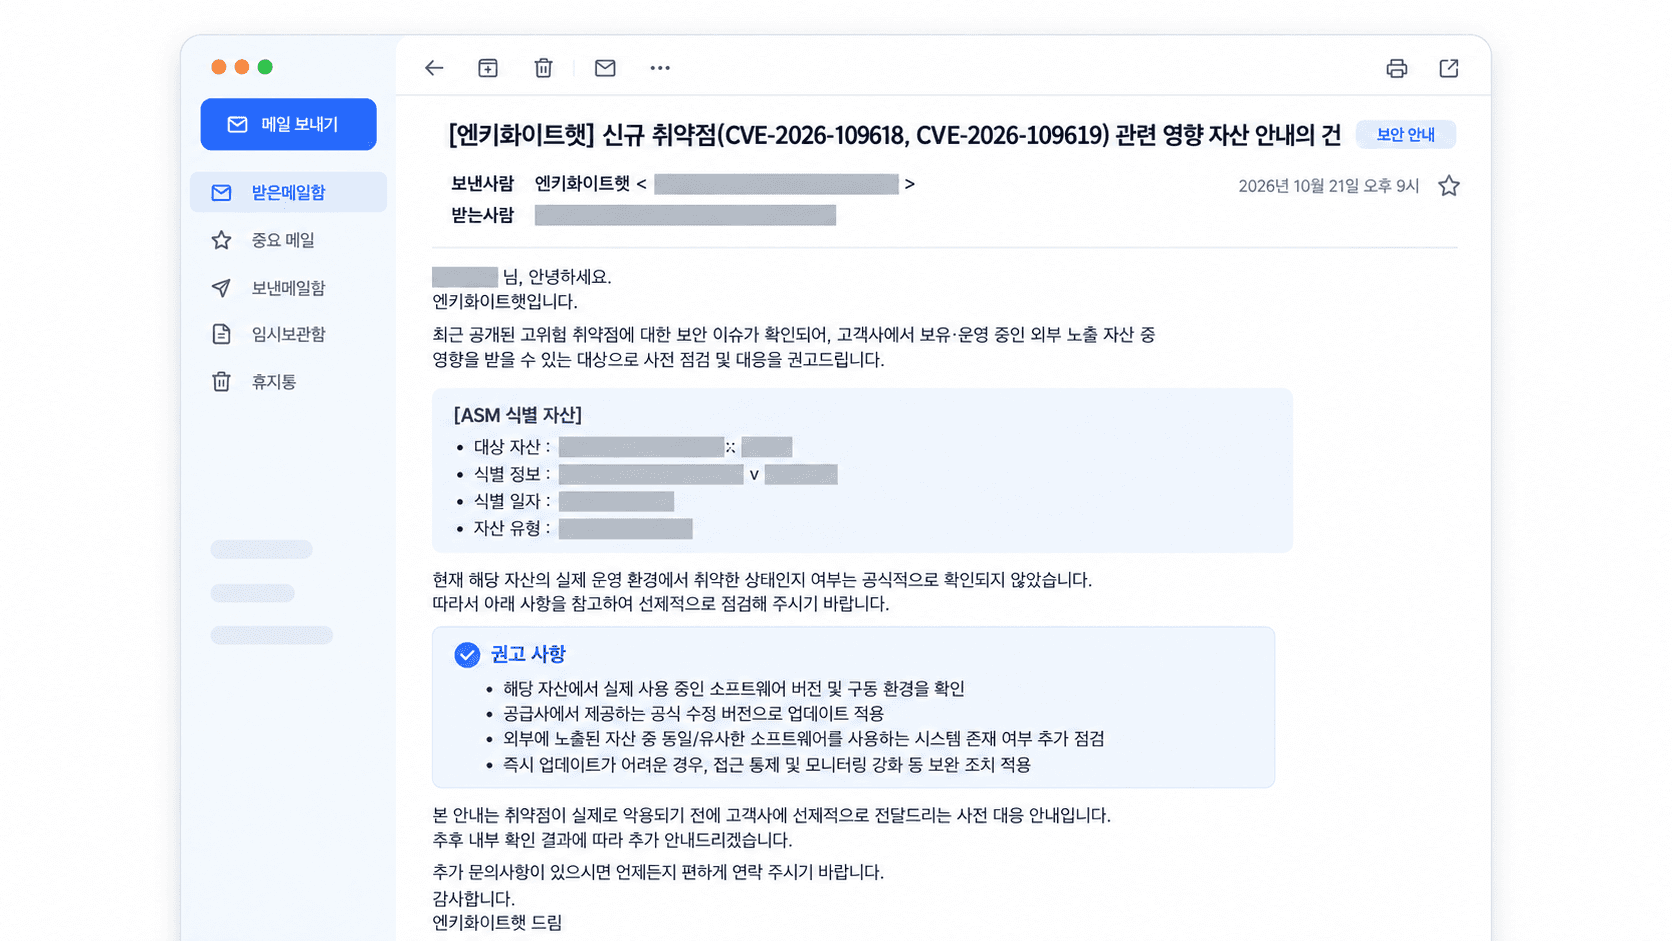
This response was possible because customer assets exposed externally, technologies used, and identified versions were already managed in the OFFen ASM platform. Based on this, Enki Whitehat reviewed research findings alongside customers' PHP usage status and quickly identified services requiring further verification.
As such, when a new security issue arises, necessary information can be delivered swiftly to clients using the technology. Customers can identify targets to inspect in their environments and proactively prepare measures needed to prevent potential damage.
Vulnerability scanner made by white hacker right after PHP2Shell release

Upon the release of the PHP2Shell vulnerability, ENKI Whitehat hackers analyzed public data and developed a scanner for clients to inspect their environments.
After the check, verify the actual PHP runtime environment and patch status, then apply necessary updates. Newly discovered services during the scan should be added to asset lists and owner records. This reduces the burden of repeating the same review process when future vulnerabilities emerge.
Use the inspection scanner provided by ENKI Whitehat to check your system directly and review required security measures. The scanner and instructions can be found at the link below.
▶ Go to PHP2Shell Vulnerability Scanner
Rapidly counter new security threats with OFFen ASM
Whenever a new critical vulnerability is released, re-inspecting all IT assets from scratch demands substantial time and resources. What is crucial is swiftly identifying and mitigating potentially affected systems based on routinely managed asset data.
ENKI Whitehat’s OFFen ASM continually identifies and manages externally exposed IT assets and technology stack data, linking them with new vulnerability intelligence to promptly detect affected assets.
This reduces the burden of re-scanning all assets from square one every time, allowing priority checks on potentially exposed assets for rapid response.

When vulnerabilities like PHP2Shell emerge, it compares identified versions with mapped tech stacks to pinpoint assets needing inspection. Security teams can act on notified assets immediately without awaiting full re-scan results.
To act fast on the next critical risk
High-risk vulnerabilities with widespread impact, such as PHP2Shell and Node2Shell, can recur repeatedly. Zero-day flaws in industry-specific software also pose a major security threat that enterprises must prepare for.
The key to responding to new vulnerabilities lies not only in actions taken after discovery, but in how accurately assets are routinely identified and managed. OFFen ASM helps organizations respond proactively and swiftly to new threats through continuous attack surface management.
If you know where in your company to check first when a vulnerability is disclosed, your response will be much faster.
▶ Inquire about ASM Solutions
Popular Articles


More Articles


" height="209.99999944452435px" id="s16LUEeu4" width="425.00001613409887px"/></svg>)